SHA-256: inspect the actual working-state evolution
Research settingIBM
The later SHA-256 working paper studies the evolution of a fully specified internal state. Its strongest contribution is a measurement protocol and a correction of earlier geometric claims, rather than a claim to break the hash function.
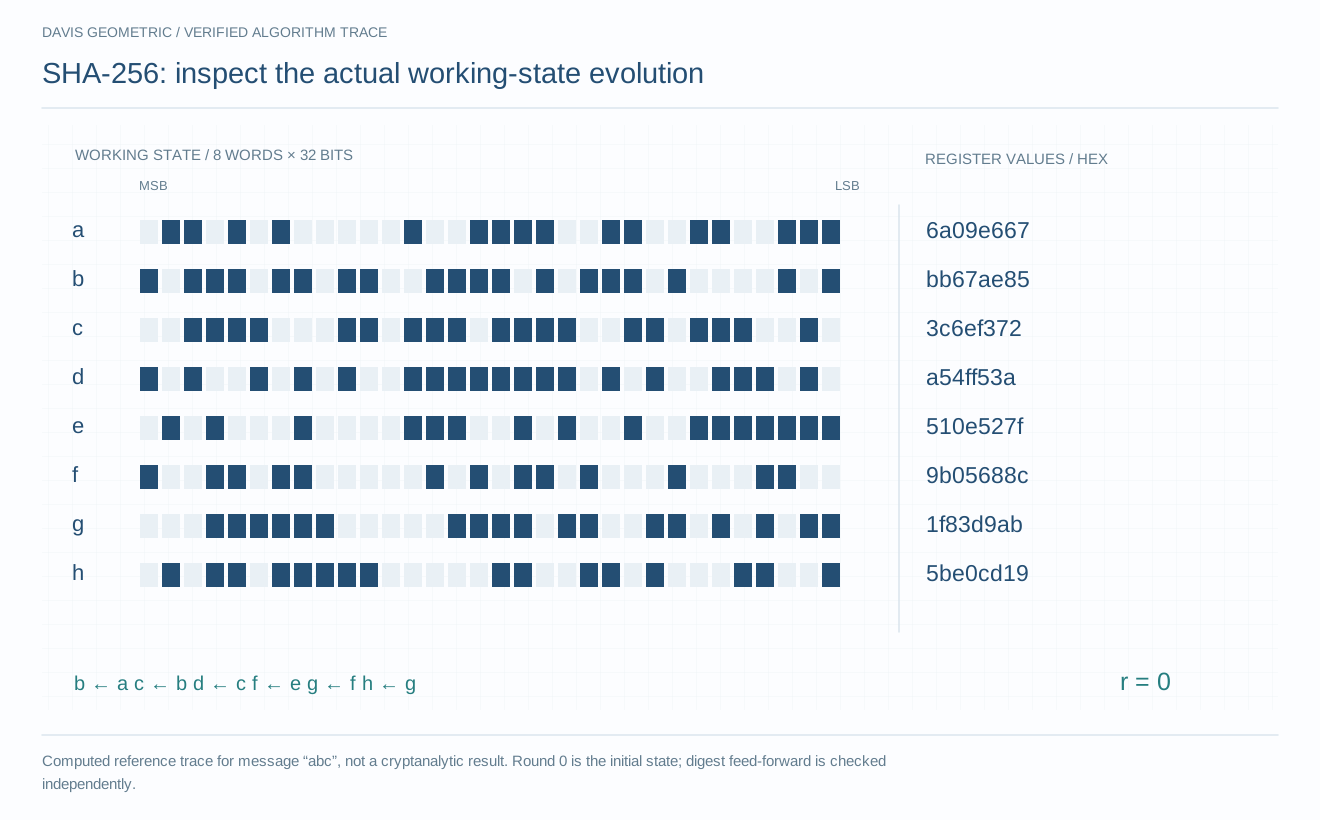
From the research record
Inspect the work
Original figures, recorded values, and explicit model details. Each exhibit identifies its source and what the comparison means.
Bit significance changes the apparent advantage
Scroll horizontally to inspect the full figure →
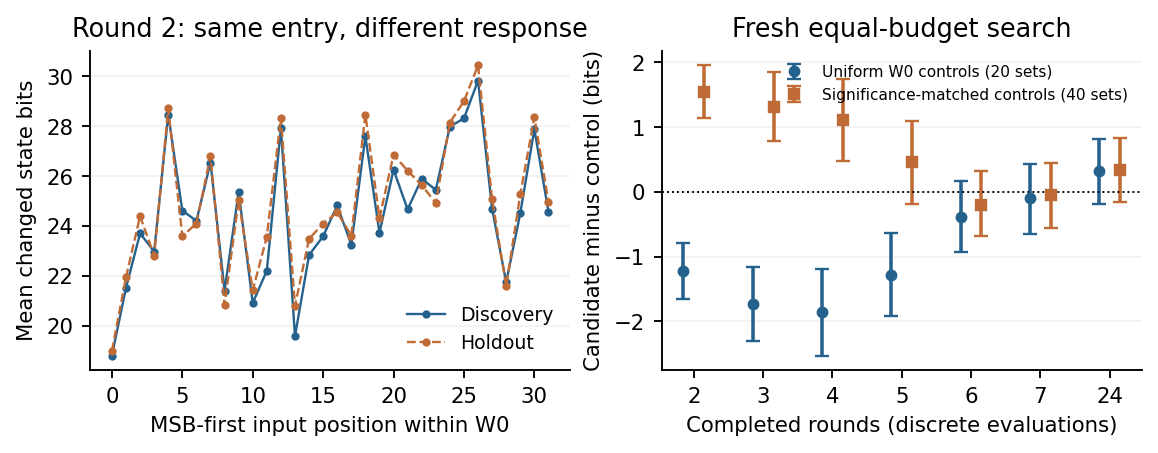
Original September 2026 figure. Left: round-2 responses at the 32 positions of W0, discovery and holdout. Right: candidate-minus-control minimum Hamming distance on 256 fresh bases; negative favors the candidate. Blue uses 20 uniform control sets, orange 40 significance-matched sets. Bars are descriptive 95% base-bootstrap intervals, conditional on the sampled sets; rounds are discrete evaluations.
early_structure.png · Original paper figure; copied without alteration
The independent holdout behind the claim
Scroll horizontally to inspect the full figure →
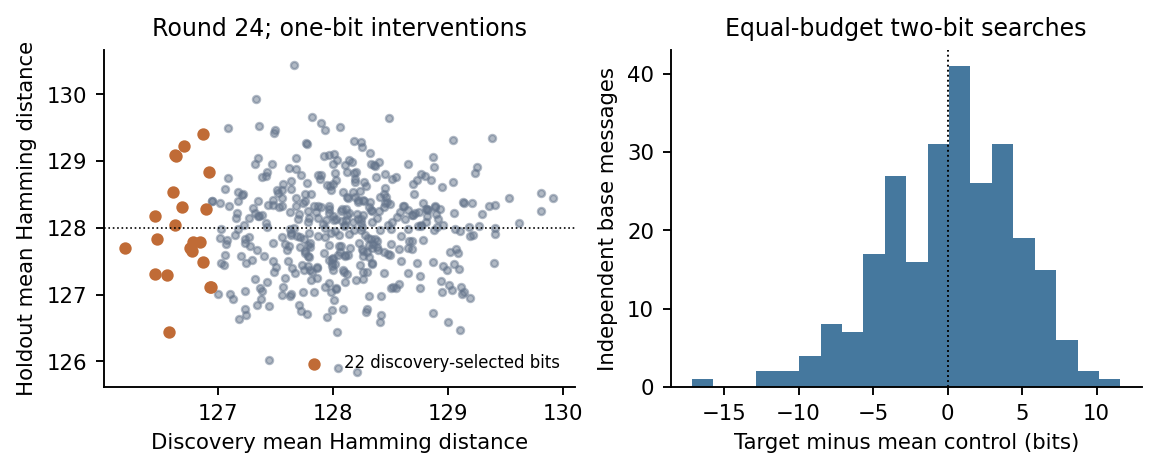
Original manuscript companion figure: all 440 selected-position comparisons and equal-budget two-bit search differences. This adds the discovery/holdout view rather than enlarging the first chart. It does not establish an attack or a digest distinguisher.
holdout_search.png · Original paper figure; copied without alteration
The round-two matched-control result
Scroll horizontally to inspect the full table →
| Comparison | Reported value |
|---|---|
| Fresh base messages | 256 |
| Patterns per six-position set per base | 15 |
| Significance-matched control sets | 40 |
| Candidate minus matched-control mean | +1.55 Hamming bits |
| Descriptive 95% base-bootstrap interval | [+1.14, +1.96] bits |
| Matched sets with lower mean minimum | 36 |
Positive values favor the controls. The candidate is worse at this endpoint after matching bit significance. This is a working-state search experiment, not a collision or preimage attack.
sha256_measurement.tex · 10 September 2026 working paper; Early structure and independent evaluation
followup_numbers.tex · MatchedSearchDiffTwo, MatchedSearchCITwo, MatchedSearchBelowTwo
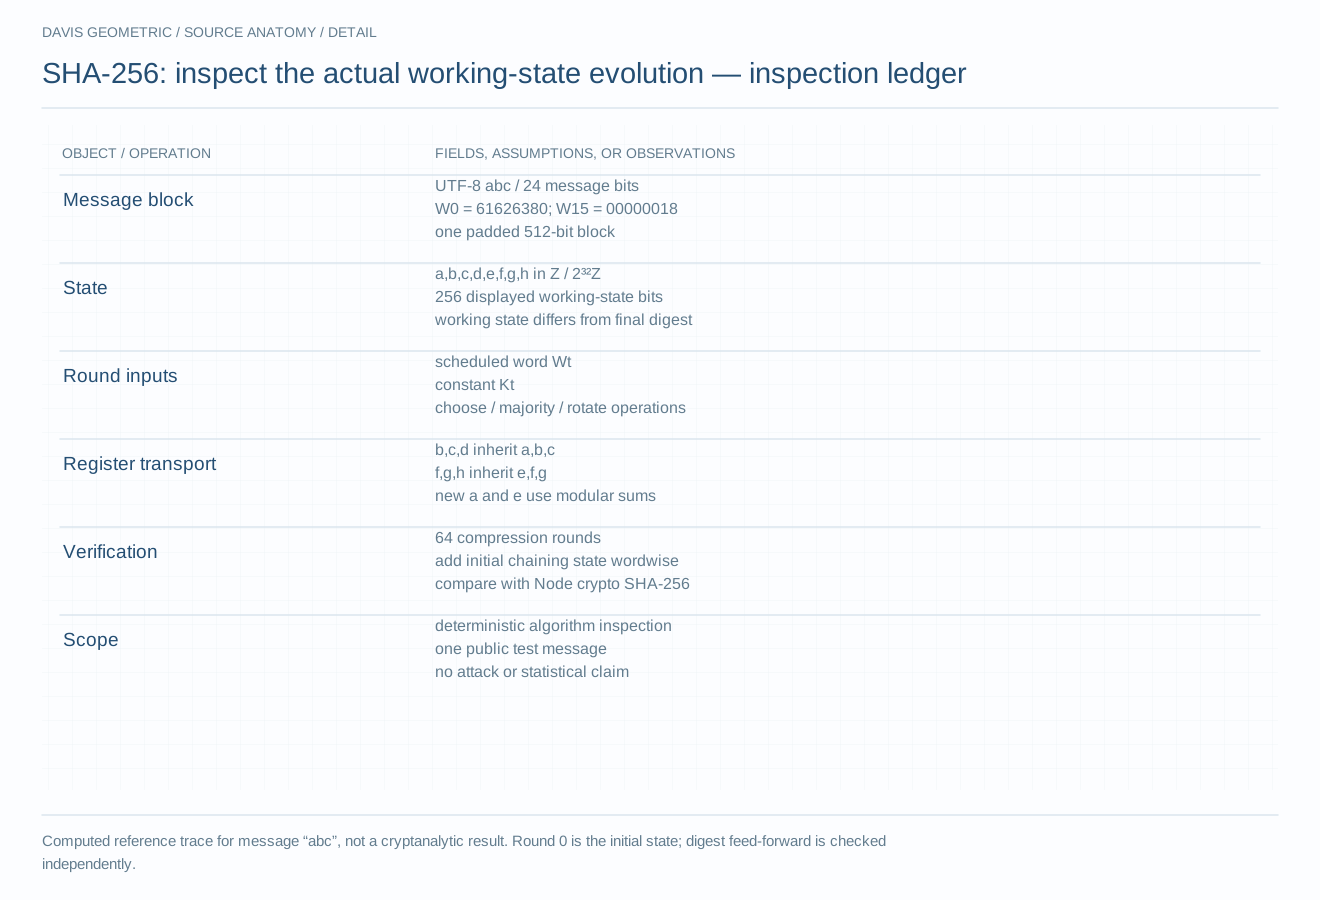
Read the technical figure
Computed reference trace for message “abc”, not a cryptanalytic result. Round 0 is the initial state; digest feed-forward is checked independently.
- Message block
-
UTF-8 abc / 24 message bits
W0 = 61626380; W15 = 00000018
one padded 512-bit block
- State
-
a,b,c,d,e,f,g,h in Z / 2³²Z
256 displayed working-state bits
working state differs from final digest
- Round inputs
-
scheduled word Wt
constant Kt
choose / majority / rotate operations
- Register transport
-
b,c,d inherit a,b,c
f,g,h inherit e,f,g
new a and e use modular sums
- Verification
-
64 compression rounds
add initial chaining state wordwise
compare with Node crypto SHA-256
- Scope
-
deterministic algorithm inspection
one public test message
no attack or statistical claim
Supporting detail
An explicit state space and an intervention
The reviewed September paper represents the eight 32-bit working registers as a 256-bit state and measures changes under declared input interventions. Hamming distance, graph spectra, and heat traces are specified observables of this representation. They do not by themselves establish intrinsic curvature or topology of SHA-256.
An exact round-one result has a direct modular-arithmetic explanation: the stated most-significant-bit intervention changes exactly two working-state bits. Later-round statistical claims need controls because bit position and input-entry timing affect the measured separation.
Why the choice of control changed the conclusion
The results digest reports an early-round candidate advantage against uniformly sampled control positions. Much of that advantage disappears or reverses when controls are matched for bit significance. The question changes from “does this subset beat random positions?” to “does it beat positions with the same simple arithmetic advantage?”
The retained record includes effects that failed to repeat, unresolved intervals, and a residual cube-statistic contrast whose cause is not established. Those distinctions make the work a more representative computational study than the older headline about a dual-torus architecture.
A measurement paper, with its correction history intact
The later paper explicitly claims no attack, distinguisher, security proof, or theorem about intrinsic SHA-256 geometry. It preserves the earlier code and withdrawn claims for audit. The old DOI below identifies that earlier work; it is not the identifier of the September revision. The revised release and evidence archives need their own public publication link.
Sources, scope, and next question
September 2026 local working paper and retained evidence digest; distinct from the earlier deposited dual-torus manuscript.
Publish the corrected release with its evidence manifest and verifier as the primary reading. Any future candidate search should predeclare an equal-budget, significance-matched comparison before interpreting a geometric pattern.
Additional source versions reviewed
-
sha-256-heat_kernel/README.mdLocal project manuscript or report · not republished here -
sha-256-heat_kernel/RESULTS.mdLocal project manuscript or report · not republished here